API Test Automation: How It Works, What to Test and Where to Start
Learn how API test automation works, which API tests to automate first, and how to build reliable coverage across schemas, auth and workflows.
An order API returns 200 OK, so the test passes.
But the total is wrong, the customer can see another user’s order, or the response no longer includes a field required by the payment service.
A successful status code tells only part of the story.
As applications become more dependent on APIs, occasional manual checks are no longer enough. Teams need a repeatable way to validate not only whether an endpoint responds, but whether it follows the expected contract, applies business rules correctly and works with the services around it.
That is where API test automation becomes valuable.
What Is API Test Automation?
API test automation uses repeatable tests to send requests to an API and verify the responses without requiring someone to perform every check manually.
An automated API test can:
- Send requests with different inputs
- Check status codes, headers and response bodies
- Validate response schemas
- Test authentication and permissions
- Confirm business rules and calculations
- Pass data between dependent requests
- Run automatically within a CI/CD pipeline
- Provide failure information when something goes wrong
Effective API automation goes beyond confirming that an endpoint is available. It checks whether the API behaves correctly under expected, unexpected and changing conditions.
Manual vs. Automated API Testing
Manual API testing remains useful when an API is new, a tester is exploring its behaviour or a team is investigating a specific problem. It gives the tester freedom to adjust requests and examine responses as they learn.
Automation becomes more valuable when the same scenarios must be checked repeatedly.
| Manual API testing | Automated API testing |
|---|---|
| Best suited to exploration and investigation | Best suited to repeatable regression coverage |
| Requests are triggered individually | Tests can run automatically and at scale |
| Results often require manual inspection | Assertions consistently validate results |
| Useful for one-time or changing checks | Useful for CI/CD and frequent releases |
Teams do not have to choose one approach exclusively. A common practice is to explore an API manually and automate important scenarios once the expected behaviour is understood.
Which API Tests Should Be Automated?
Trying to automate every possible request from the beginning usually creates unnecessary work. Start with scenarios that are business-critical, performed frequently or likely to cause serious problems if they fail.
Functional and Business-Rule Tests
Functional tests verify that an endpoint performs its intended operation.
For an order API, this could mean confirming that a valid request creates an order with the correct product, quantity, price, tax and initial status.
The test should validate the result—not just the response code.
Negative and Error-Handling Tests
Negative tests show what happens when the API receives invalid or incomplete information.
Useful scenarios include:
- Missing required fields
- Incorrect data formats
- Unsupported values
- Quantities outside permitted limits
- Requests for records that do not exist
- Duplicate submissions
A well-designed API should fail predictably and return an error that helps the consumer understand what went wrong.
Schema and Contract Tests
Schema tests verify that an API response follows the expected structure. They can check whether required fields are present, values use the correct data types and the response remains consistent with the published API contract.
These checks can identify breaking changes even when the endpoint continues to return a successful status.
Authentication and Authorization Tests
Authentication confirms the identity making a request. Authorization determines what that identity is permitted to do.
Automated coverage should confirm that valid credentials work while missing, invalid or expired credentials are rejected. It should also verify that users cannot access another customer’s information or perform operations restricted to a different role.
Connected Workflow Tests
Business processes frequently involve several endpoints. An order workflow might authenticate a user, create an order, retrieve it and then cancel it.
Testing these requests together can reveal dependency and data-flow problems that isolated endpoint checks may not detect.
Basic response-time checks can also be automated, but full load and scalability testing generally requires a separate performance-testing strategy.
A Practical Order-Management API Example
Consider an order service with four endpoints:
POST /orderscreates an orderGET /orders/{id}retrieves itPATCH /orders/{id}updates itDELETE /orders/{id}cancels it
A basic automated test could submit a valid order and look for a successful response. Useful coverage, however, would include several related scenarios.
Successful Order Creation
The test submits valid customer, product and delivery details, then verifies:
- The expected response status
- A newly generated order ID
- The correct product and quantity
- Accurate price and tax calculations
- The expected initial status
- Conformance with the response schema
Invalid Order Data
Another test submits an invalid product code, a quantity of zero or a request with missing customer information. It confirms that the API rejects the request with the correct error and does not create an invalid order.
Permission Validation
A customer account and an administrator account attempt the same restricted operation. The test confirms that only the authorized role can perform it and that the response does not expose sensitive information.
Complete Order Workflow
The automated workflow can:
- Authenticate the user.
- Create an order.
- Capture the generated order ID.
- Retrieve the order using that ID.
- Confirm that the stored information matches the original request.
- Cancel the order.
- Verify that its final status is cancelled.
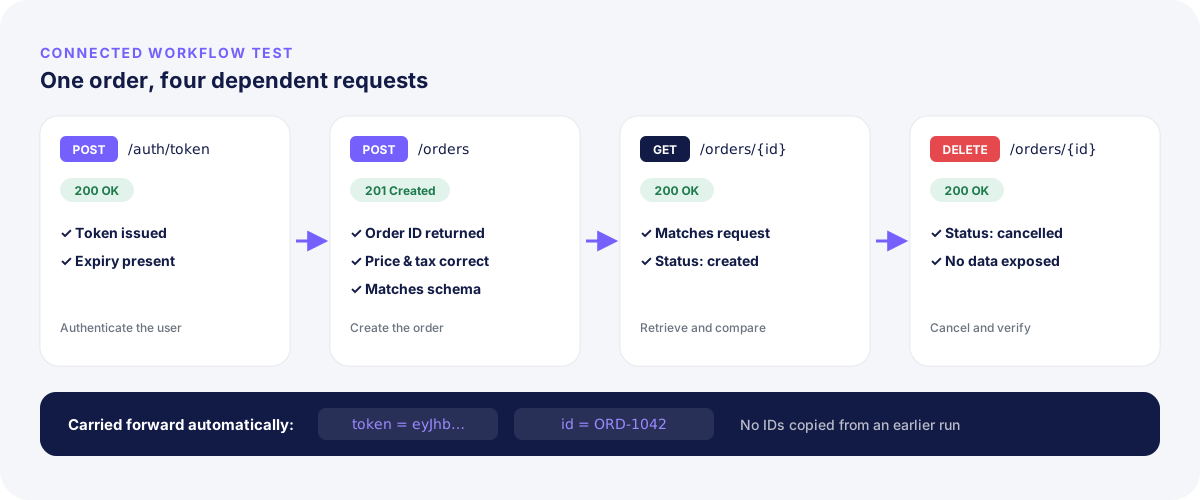
This tests a recognisable business process instead of treating every endpoint as an unrelated request.
How API Test Automation Works
Most API automation follows a similar process.
First, the team identifies the available endpoints and expected behaviour. This information may come from an OpenAPI specification, technical documentation, business requirements or observed API traffic.
Tests are then created with the required request data, authentication details and assertions. Each assertion defines what the API must return or what business condition must be true.
During execution, dynamically generated values such as access tokens, customer IDs and order IDs can be saved and passed into later requests.
Finally, the results are returned to the team or delivery pipeline. A useful result should show:
- Which request failed
- What the test expected
- What the API returned
- Where the failure occurred in the workflow
- Enough context to begin investigating
Without that context, teams may spend more time reconstructing the failure than running the test.
Managing Test Data and Dependent Requests
Test data is a common source of unreliable API tests.
A hardcoded customer or order might already exist, be changed by another test or become invalid over time. Conflicts become more likely when multiple tests run in parallel against a shared environment.
Where possible, each test should create the data it needs. Unique values can be generated for users, orders and transactions, with temporary records removed after execution.
Environment-specific URLs, credentials and configuration should also remain separate from test logic. Credentials must be managed securely rather than stored directly in test files.
For dependent requests, data should be passed dynamically. If one request creates an order, the returned order ID should be used by the retrieval and cancellation requests. The workflow should not depend on an ID copied from an earlier run.
Running API Tests in CI/CD
API tests provide the most value when they run close to the changes they evaluate.
A small suite covering critical services and workflows might run on every pull request or deployment. A broader regression suite can run before a release or on a schedule.
Before using test results as a quality gate, teams should decide:
- Which tests are important enough to block a deployment
- Which environment should be tested
- How secrets and test data will be managed
- Who owns the investigation when a test fails
- How unavailable external dependencies will be handled
Quality gates should reflect business risk and test reliability. If unstable tests repeatedly block releases, teams may begin ignoring failures or rerunning pipelines until they pass.
Common API Automation Mistakes
Checking Only the Status Code
A successful response does not prove that the data, calculations or resulting business state are correct. Tests should validate the response content and its effect.
Testing Endpoints Without Workflows
Endpoint-level tests are important, but they may miss failures between dependent services. Critical business workflows should also be tested from request to outcome.
Hardcoding Data and Credentials
Fixed records create conflicts, while embedded credentials introduce security risks. Use generated data, environment configuration and secure secrets management.
Covering Only the Happy Path
Valid requests show that the API can work. Negative, boundary and permission tests show whether it behaves safely when something is wrong.
Using Retries to Hide Failures
Retries may be appropriate for a known temporary dependency problem. They should not become the default response to unreliable tests or genuine defects.
Applying Unreliable Quality Gates
A pipeline should not be blocked by tests the team does not trust. Stabilise critical tests and align gates with release risk before making them mandatory.
How to Evaluate an API Automation Platform
When comparing platforms, consider whether they can:
- Create tests from OpenAPI specifications or existing API activity
- Generate and manage realistic test data
- Validate schemas, business rules and error responses
- Handle authentication and authorization scenarios
- Connect requests into dependent workflows
- Run within existing CI/CD pipelines
- Provide useful failure context
- Support configurable quality gates
The right platform should reduce the effort required to create, run and maintain meaningful API coverage. It should do more than make sending requests easier.
How Nogrunt Supports API Test Automation
Nogrunt helps teams turn API information into repeatable automated coverage.
Tests can be generated from OpenAPI specifications or observed traffic, reducing the need to build every scenario manually. Nogrunt also supports test-data generation and validation across schemas, authentication behaviour and error-handling paths.
For processes involving multiple endpoints, connected API workflows can carry relevant information from one request to the next. Tests can run within CI/CD pipelines, where configurable quality gates help teams evaluate whether a build should move forward.
When a test fails, Nogrunt provides context to help QA and engineering teams understand the request, response and affected workflow without manually recreating every step.
The goal is not simply to run more API tests. It is to build useful coverage, reduce repetitive setup and provide clearer release feedback.
Frequently Asked Questions
What is API test automation?
API test automation uses repeatable tests to send requests and verify responses, schemas, business rules, permissions and connected workflows without requiring every check to be performed manually.
Which API tests should be automated first?
Start with critical business workflows, frequently repeated regression checks, authentication rules, error-handling scenarios and services whose failure would significantly affect users or connected systems.
Can tests be generated from an OpenAPI specification?
Yes. An OpenAPI specification provides endpoints, parameters and response structures that can support initial test generation. Business rules, negative scenarios and expected outcomes may still require additional context and human review.
How are automated API tests used in CI/CD?
API tests can run when code is committed, a build is created or an application is deployed. Their results can provide rapid feedback or prevent a release from progressing when a critical check fails.
Start with the Workflows That Matter
API test automation does not have to begin with every endpoint and every possible input.
Start with a few critical workflows. Validate their successful paths, error handling, permissions and data contracts. Once those tests are stable, expand coverage based on business risk, product changes and previous failures.
A useful API automation suite should help the team decide whether its services are ready to release—not simply produce a larger number of passing tests.
See how Nogrunt can help your team turn API specifications into automated coverage across connected workflows and CI/CD pipelines.
Book a demo